$39 Billion in Fraud-Linked Assets: Inside the UAE-Led Operation Targeting Global Scam Networks
An international operation led by the UAE targeted organised digital fraud networks across 30 countries. Explore the reported results, the role of intelligence sharing and the implications for businesses combating online scams.
AbuseOne Editorial Team
6 min read
30 countries. More than 960 arrests. Over 123 million reported thwarted fraud attempts. A coordinated international effort to disrupt digital crime.
Organised digital fraud is no longer confined to individual scammers operating behind anonymous accounts. Today's fraud networks can span multiple countries, exploit digital platforms, manipulate victims and move money through complex financial channels.
An international operation led by the United Arab Emirates has highlighted the scale of the challenge and what coordinated action between law enforcement, technology companies and financial institutions can achieve.
Known as Operation Confrontation Ghost, the initiative brought together law enforcement authorities from 30 countries, international organisations and private-sector partners to target organised digital fraud.
According to figures released by UAE sources, the operation identified more than $39 billion in funds and digital assets linked to fraudulent activities, while reporting the disruption of millions of attempted scams worldwide.
The results illustrate an important shift in fraud prevention: tackling organised digital crime increasingly depends on international intelligence sharing, financial tracing and coordinated action across multiple platforms.
Inside Operation Confrontation Ghost
Led by the UAE Ministry of Interior, Operation Confrontation Ghost focused on emerging forms of digital crime, including AI-enabled fraud, financial scams conducted through digital platforms and technology-facilitated sexual extortion.
The operation combined law enforcement coordination with contributions from technology and financial services companies.
The reported results include:
- More than $39 billion in funds and digital assets identified as linked to fraudulent activities, with recovery efforts ongoing.
- More than 960 arrests reported by participating authorities.
- Over 3,500 suspects identified for further investigation.
- Approximately 15,500 victims identified.
- More than 9,000 intelligence exchanges between participating parties.
- 4,126 bank accounts blocked.
- More than 570 fraud-related social media accounts or channels closed.
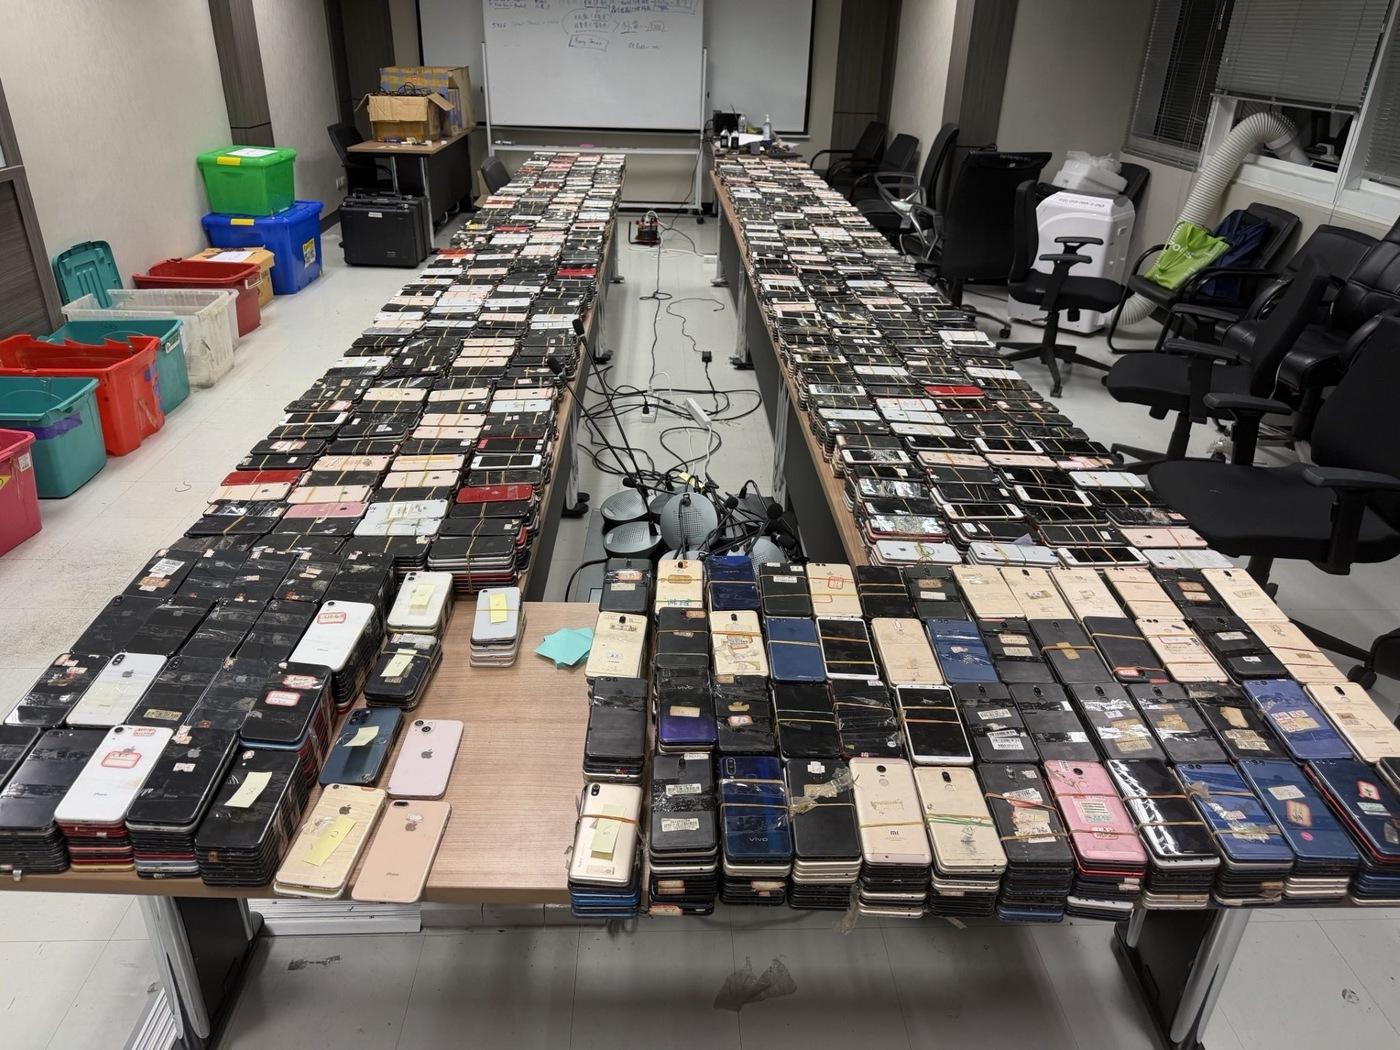
- 29 suspected fraud centres raided.
- More than 123.71 million attempted cyber-fraud incidents reportedly thwarted worldwide.
The operation also reported security measures involving more than four billion financial transactions per month, supported by tokenisation technology.
These figures were reported by UAE sources and media covering the announcement. They represent different types of outcomes, from investigative leads and enforcement actions to fraud-prevention activity, and should not be interpreted as a single measure of recovered funds or proven criminal liability.
Why $39 Billion in Fraud-Linked Assets Matters
The figure that stands out is the reported $39 billion associated with fraudulent activity.
However, identifying assets linked to suspected fraud is not the same as recovering them. Authorities and participating organisations are still working to recover the identified assets.
That distinction matters because financial investigations often involve multiple jurisdictions, financial institutions and digital payment channels. Investigators may need to establish ownership, trace the movement of funds, preserve evidence and work through the relevant legal processes before assets can be frozen or returned.
The scale of the reported figure illustrates why financial intelligence is a central component of modern fraud investigations.
Following the money can help investigators connect individual incidents to wider networks, identify intermediaries and establish links between suspicious transactions and suspected criminal activity.
The Role of Intelligence Sharing
One of the operation's most significant reported outcomes was the exchange of more than 9,000 pieces of intelligence.
Fraud networks often exploit gaps between jurisdictions and organisations. A suspicious account identified in one country may be connected to a fraudulent website hosted elsewhere, a social media account targeting victims in another market and a financial intermediary operating across several regions.
No single organisation necessarily has the complete picture.
Intelligence sharing can help connect these separate elements, allowing participating authorities and companies to identify patterns, prioritise investigations and coordinate responses more effectively.
The operation involved INTERPOL, the Global Anti-Scam Alliance (GASA) and partners from the private, technology and financial services sectors.
The collaboration demonstrates the importance of bringing together different forms of expertise. Law enforcement authorities have investigative and enforcement powers, while private-sector organisations may hold relevant information about accounts, platforms, transactions or suspicious digital activity.
Effective cooperation must still respect applicable laws, privacy requirements and the rules governing the sharing of sensitive information.
AI, Digital Platforms and the Changing Nature of Fraud
The operation targeted several forms of digital crime, including AI-enabled fraud and financial scams conducted through online platforms.
Artificial intelligence can make fraudulent communications more convincing, automate parts of a scam operation and help criminals adapt their tactics at scale. Social media, messaging services and digital payment systems can also be exploited to reach victims and move money quickly.
These developments create challenges for both investigators and businesses.
Fraudulent activity may involve impersonation accounts, deceptive advertisements, fake websites, manipulated identities or coordinated campaigns that cross multiple platforms. Individual incidents can appear unrelated until researchers connect the available evidence.
This is where digital investigations and open-source intelligence (OSINT) can contribute.
By analysing publicly available information, documenting suspicious activity and establishing links between digital entities, researchers can help organisations identify potential fraud patterns and develop actionable leads.
Such findings require careful verification. A digital connection or suspicious indicator may justify further investigation, but it does not automatically establish criminal wrongdoing.
From Detection to Disruption
Identifying suspected fraud is only one stage of an effective response.
The wider process may involve documenting evidence, identifying affected parties, reporting suspicious activity, tracing relevant financial flows and coordinating with organisations that have the authority or capability to act.
The reported blocking of more than 4,000 bank accounts and closure of hundreds of fraud-related social media channels illustrates the range of interventions that can follow an investigation.
Different cases require different responses. Some may call for platform enforcement, others for financial controls or formal law enforcement investigations. In each instance, the quality of the underlying information can influence the effectiveness of the response.
For businesses, this reinforces the importance of having a structured process for receiving reports, assessing evidence, prioritising threats and escalating credible findings.
What This Means for Businesses
Although Operation Confrontation Ghost was an international law enforcement initiative, its implications extend to businesses exposed to online fraud and digital abuse.
Organisations may encounter fake websites using their brand, impersonation accounts targeting their customers, fraudulent advertisements, scam campaigns or other activity that damages trust and creates financial losses.
Responding effectively requires more than identifying an isolated incident. Businesses need reliable information that helps them understand the nature of a threat, assess its potential impact and determine the appropriate next step.
Independent researchers can contribute by identifying suspicious activity, documenting evidence and connecting relevant information from public sources.
When combined with appropriate verification and clear reporting channels, this research can support better-informed decisions and more effective responses.
How AbuseOne Fits Into the Fight Against Digital Fraud
AbuseOne focuses on connecting businesses with independent researchers working on online fraud, digital scams and online abuse.
Through its researcher network and fraud-intelligence approach, the platform aims to help organisations identify suspicious activity, obtain documented findings and turn research into actionable intelligence.
The broader lesson from Operation Confrontation Ghost is that combating organised digital fraud requires cooperation between people and organisations with different capabilities.
Law enforcement, financial institutions, technology companies and independent investigators each have distinct roles. Connecting credible information with the organisations able to act on it can help strengthen the overall response.
As fraud networks continue to operate across borders and digital platforms, access to reliable intelligence and investigative expertise will remain essential.
The challenge is not simply to identify more fraud. It is to connect the evidence, expertise and action needed to disrupt it.
Sources and attribution
- Emirates News Agency (WAM)Operation Confrontation Ghost(opens in a new tab)
- Khaleej TimesUAE international operation targeting fraud networks(opens in a new tab)
About AbuseOne
AbuseOne connects businesses with independent researchers focused on online fraud, digital scams, OSINT and online abuse. Learn more at abuseone.com (opens in a new tab).
- Online fraud
- Financial intelligence
- Intelligence sharing
- Scam networks
- Law enforcement
- OSINT